Real-time data protection for the modern endpoint
Protect source code, customer data, and the systems your engineers reach from the terminal.
Bold runs AI on the device to classify data by meaning and stop risky actions before data leaves.
Why the endpoint
In the AI era, more and more work happens directly on the device. Especially engineering work.
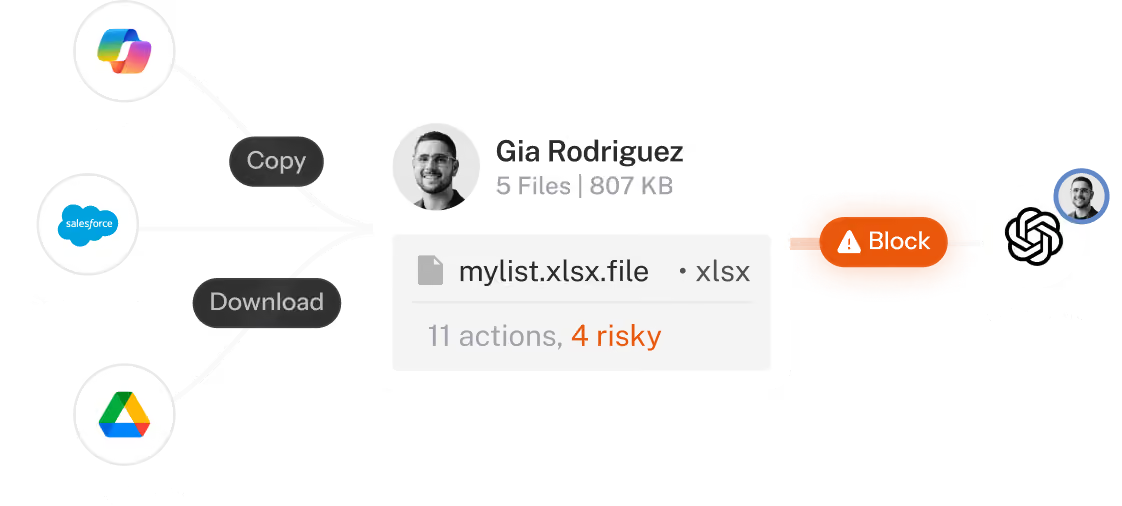
Code gets cloned, customer data gets exported for debugging, and AI assistants and MCPs reach both, creating exposure.
An engineer pushes a service repository to a personal GitHub account.
A coding agent moves repository data with no human at the keyboard.
A support engineer exports customer tenant data locally to reproduce a bug.

An MCP connection follows someone into a personal account mid-session.
The endpoint is the one layer where data sensitivity, intention, and the action itself come together.
Controlling risk there is what makes prevention possible before code or customer data leaves.
Where Bold fits
Bold runs alongside the security investments you already have and reaches the data risk those tools cannot.

What Bold delivers
Accidental exposure, insider misuse, and data headed to personal accounts stop at the moment of action, not after.
Code pushed to personal repositories and credentials sitting in terminal history are visible to Bold. Tools that only watch the browser never see either.

Proprietary source, architecture documentation, model artifacts, and customer tenant data, classified by meaning, not pattern matching.
Shadow AI, unmanaged accounts, and the MCP connections other tools miss, inventoried on the device rather than stitched together from logs.
No file content is sent anywhere, so source code is never exposed to a third-party cloud in order to be classified. Developer privacy survives the deployment.
Behavioral history, data interaction detail, and lineage arrive already attached to the incident.
Copilot reached through a personal GitHub account looks the same as the corporate one to everything else in your stack. Not to Bold.
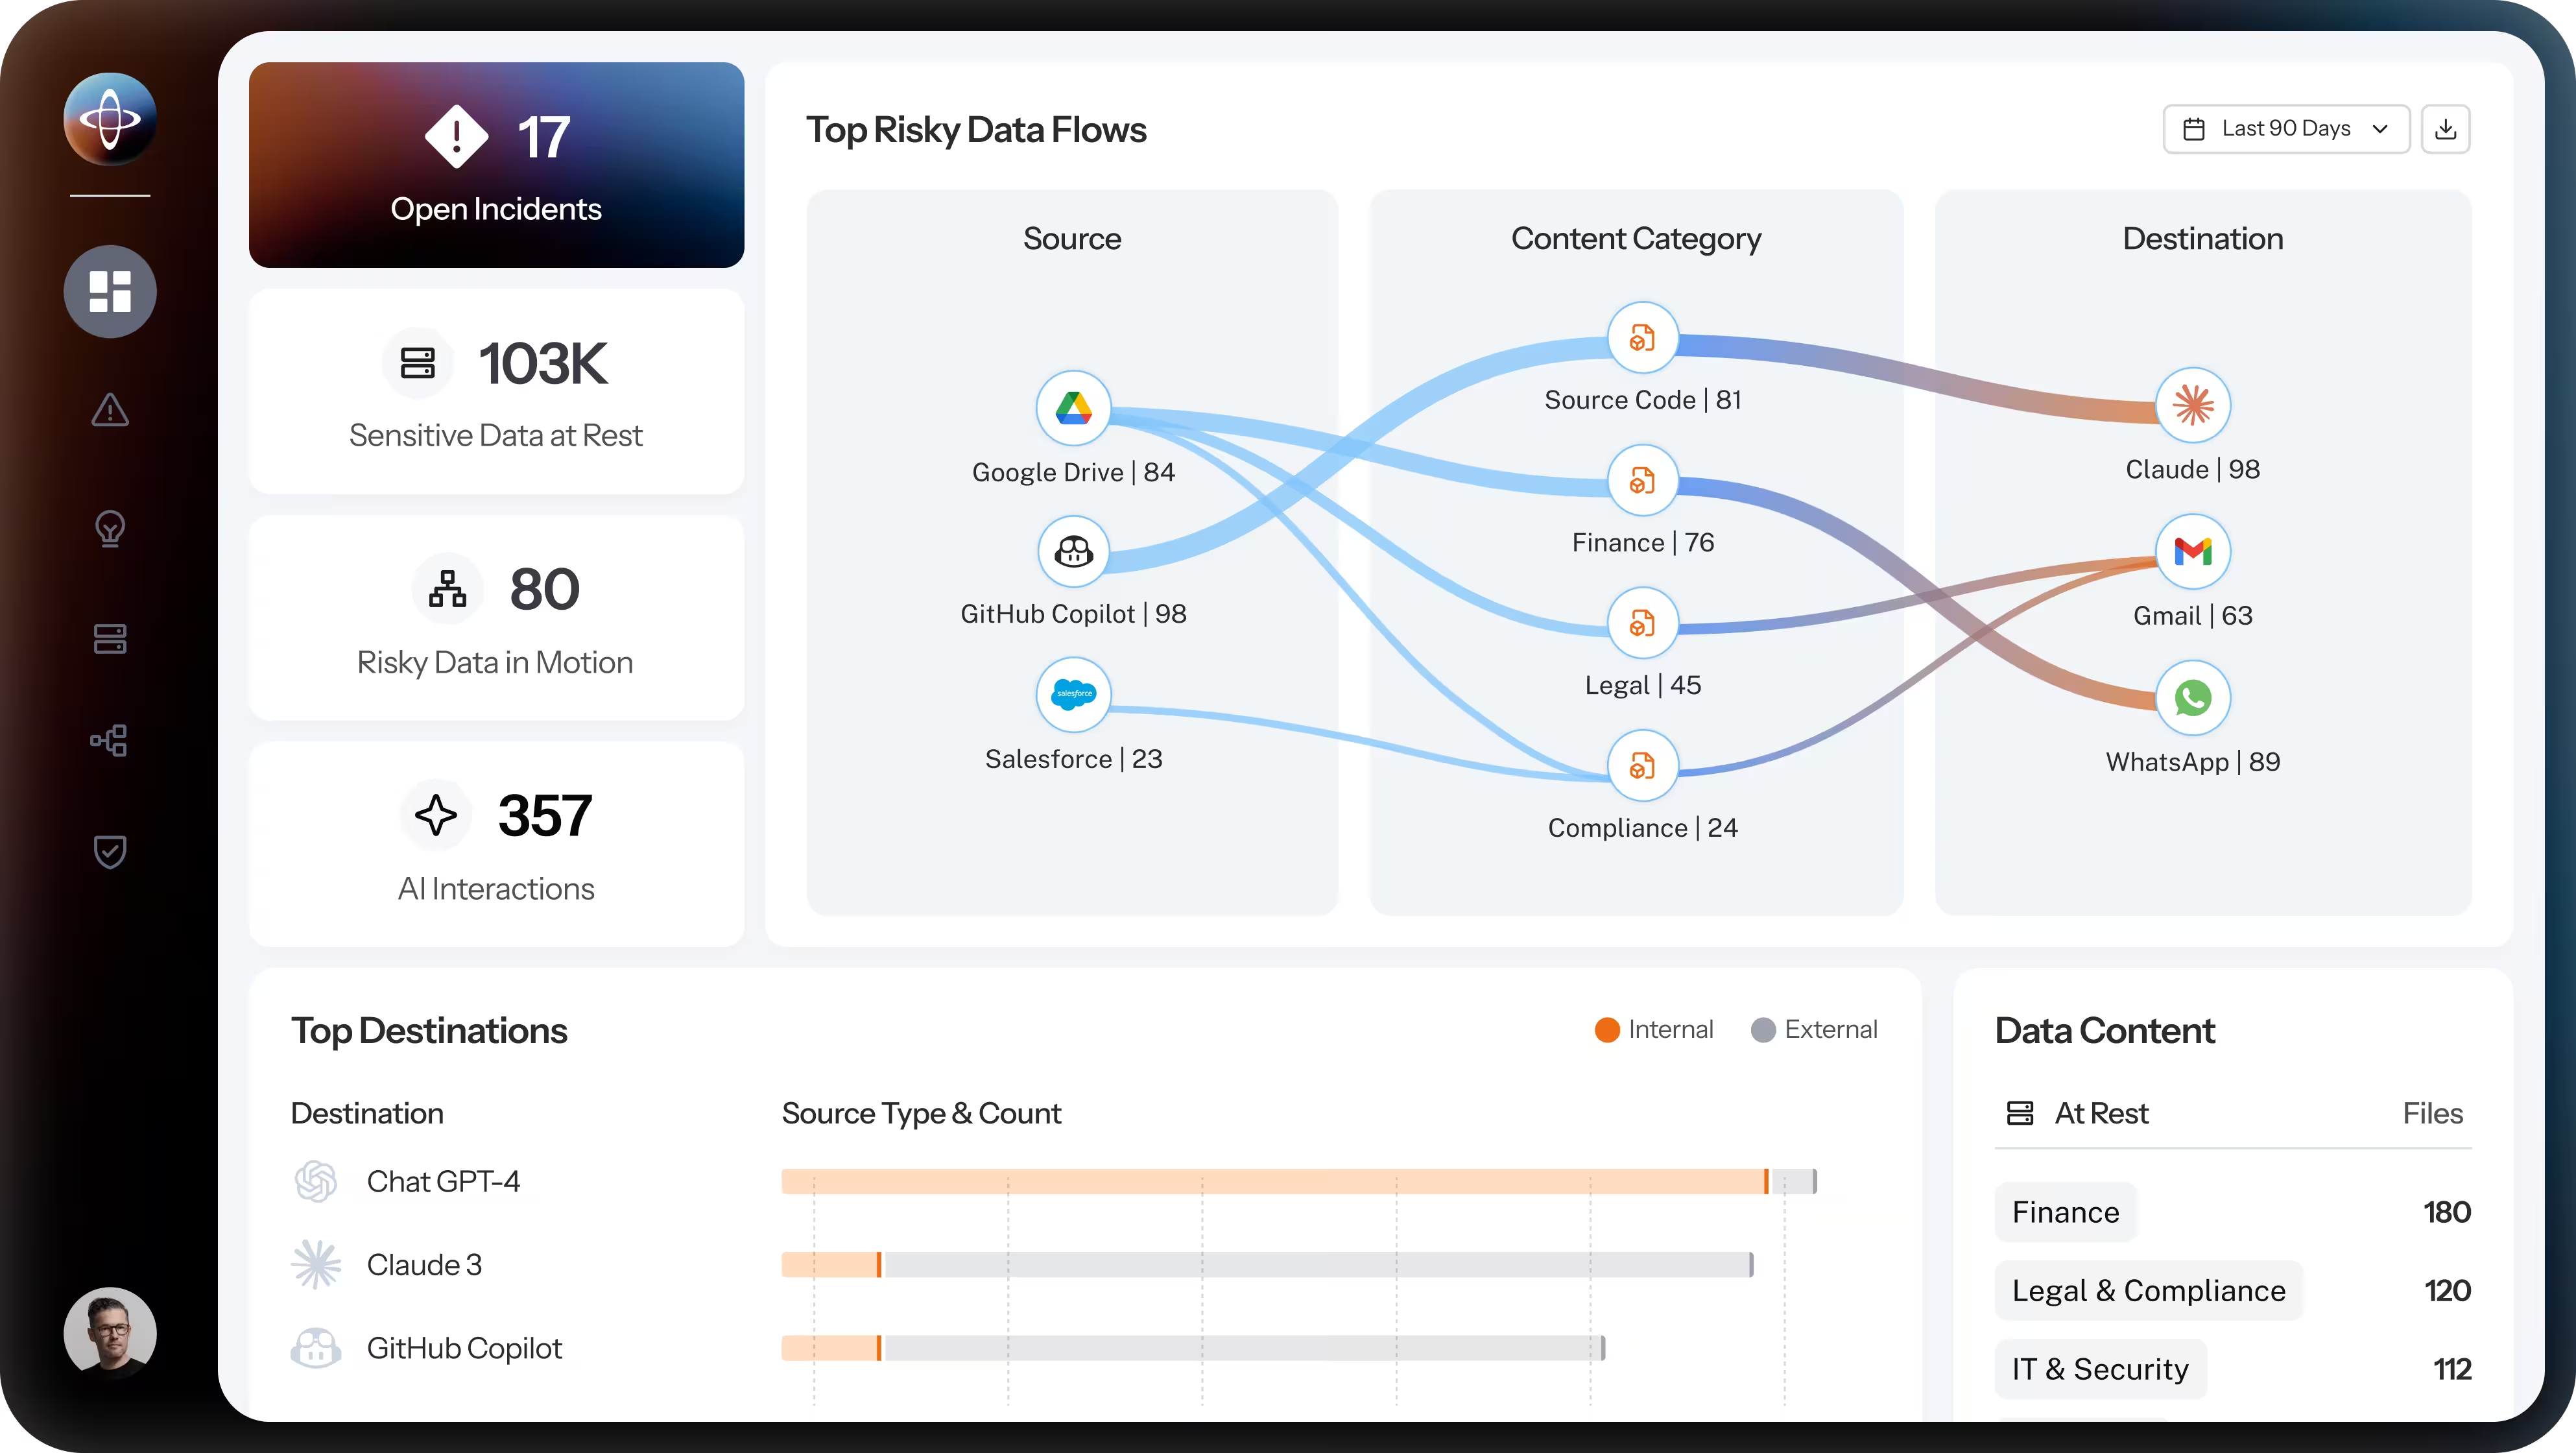
How Bold works
Bold runs AI locally to understand data, analyze intention, and prevent risk in real time.

See every repo, terminal, and AI session
Bold lives on the endpoint and sees everything: every channel, every app, every file, every workflow. No API gaps, no blind spots, including the CLI and the desktop apps network tools cannot see.
Know what the code is and why it is moving
Bold's AI classifies data by meaning and reads the intention behind every action: whether a file is proprietary source or public dependency, where it came from, who is moving it, their role, and their risk profile.
Stop the push before it leaves
Bold acts in real time, redirecting a repository headed for a personal account or blocking customer data on its way to an unmanaged AI tool. Most risk is stopped before it ever becomes an alert to triage.
Investigate without rebuilding the story
When something does need review, Bold has the full picture: what the data was, who moved it, where it went. Investigations that took days close in minutes.
Built for high-access engineering teams
Even where access is deliberate and well governed, risk still appears at the moment of action:
Code and credentials moving through the terminal
Approved tools used in ways policy cannot anticipate
New AI tools adopted before security teams hear about them

Coding agents acting with repository access and no human present

Support and services teams working inside customer environments
Customer tenant data exported locally for debugging
The outcome
Bold prevents the most common and most consequential forms of exposure at the moment they happen, gives insider risk investigations the data context they have been missing, and protects source code and customer data at rest and in motion on every device. For a company built on customer trust, that control is foundational.
One platform, three use cases
Endpoint DLP
AI Usage Control
Endpoint Insider Risk