AI Usage Control
AI usage control that governs data, not just tools
Bold runs AI on the device to see every AI interaction and stop sensitive data before it leaves through AI tools.
Your controls went blind
when AI moved to the device
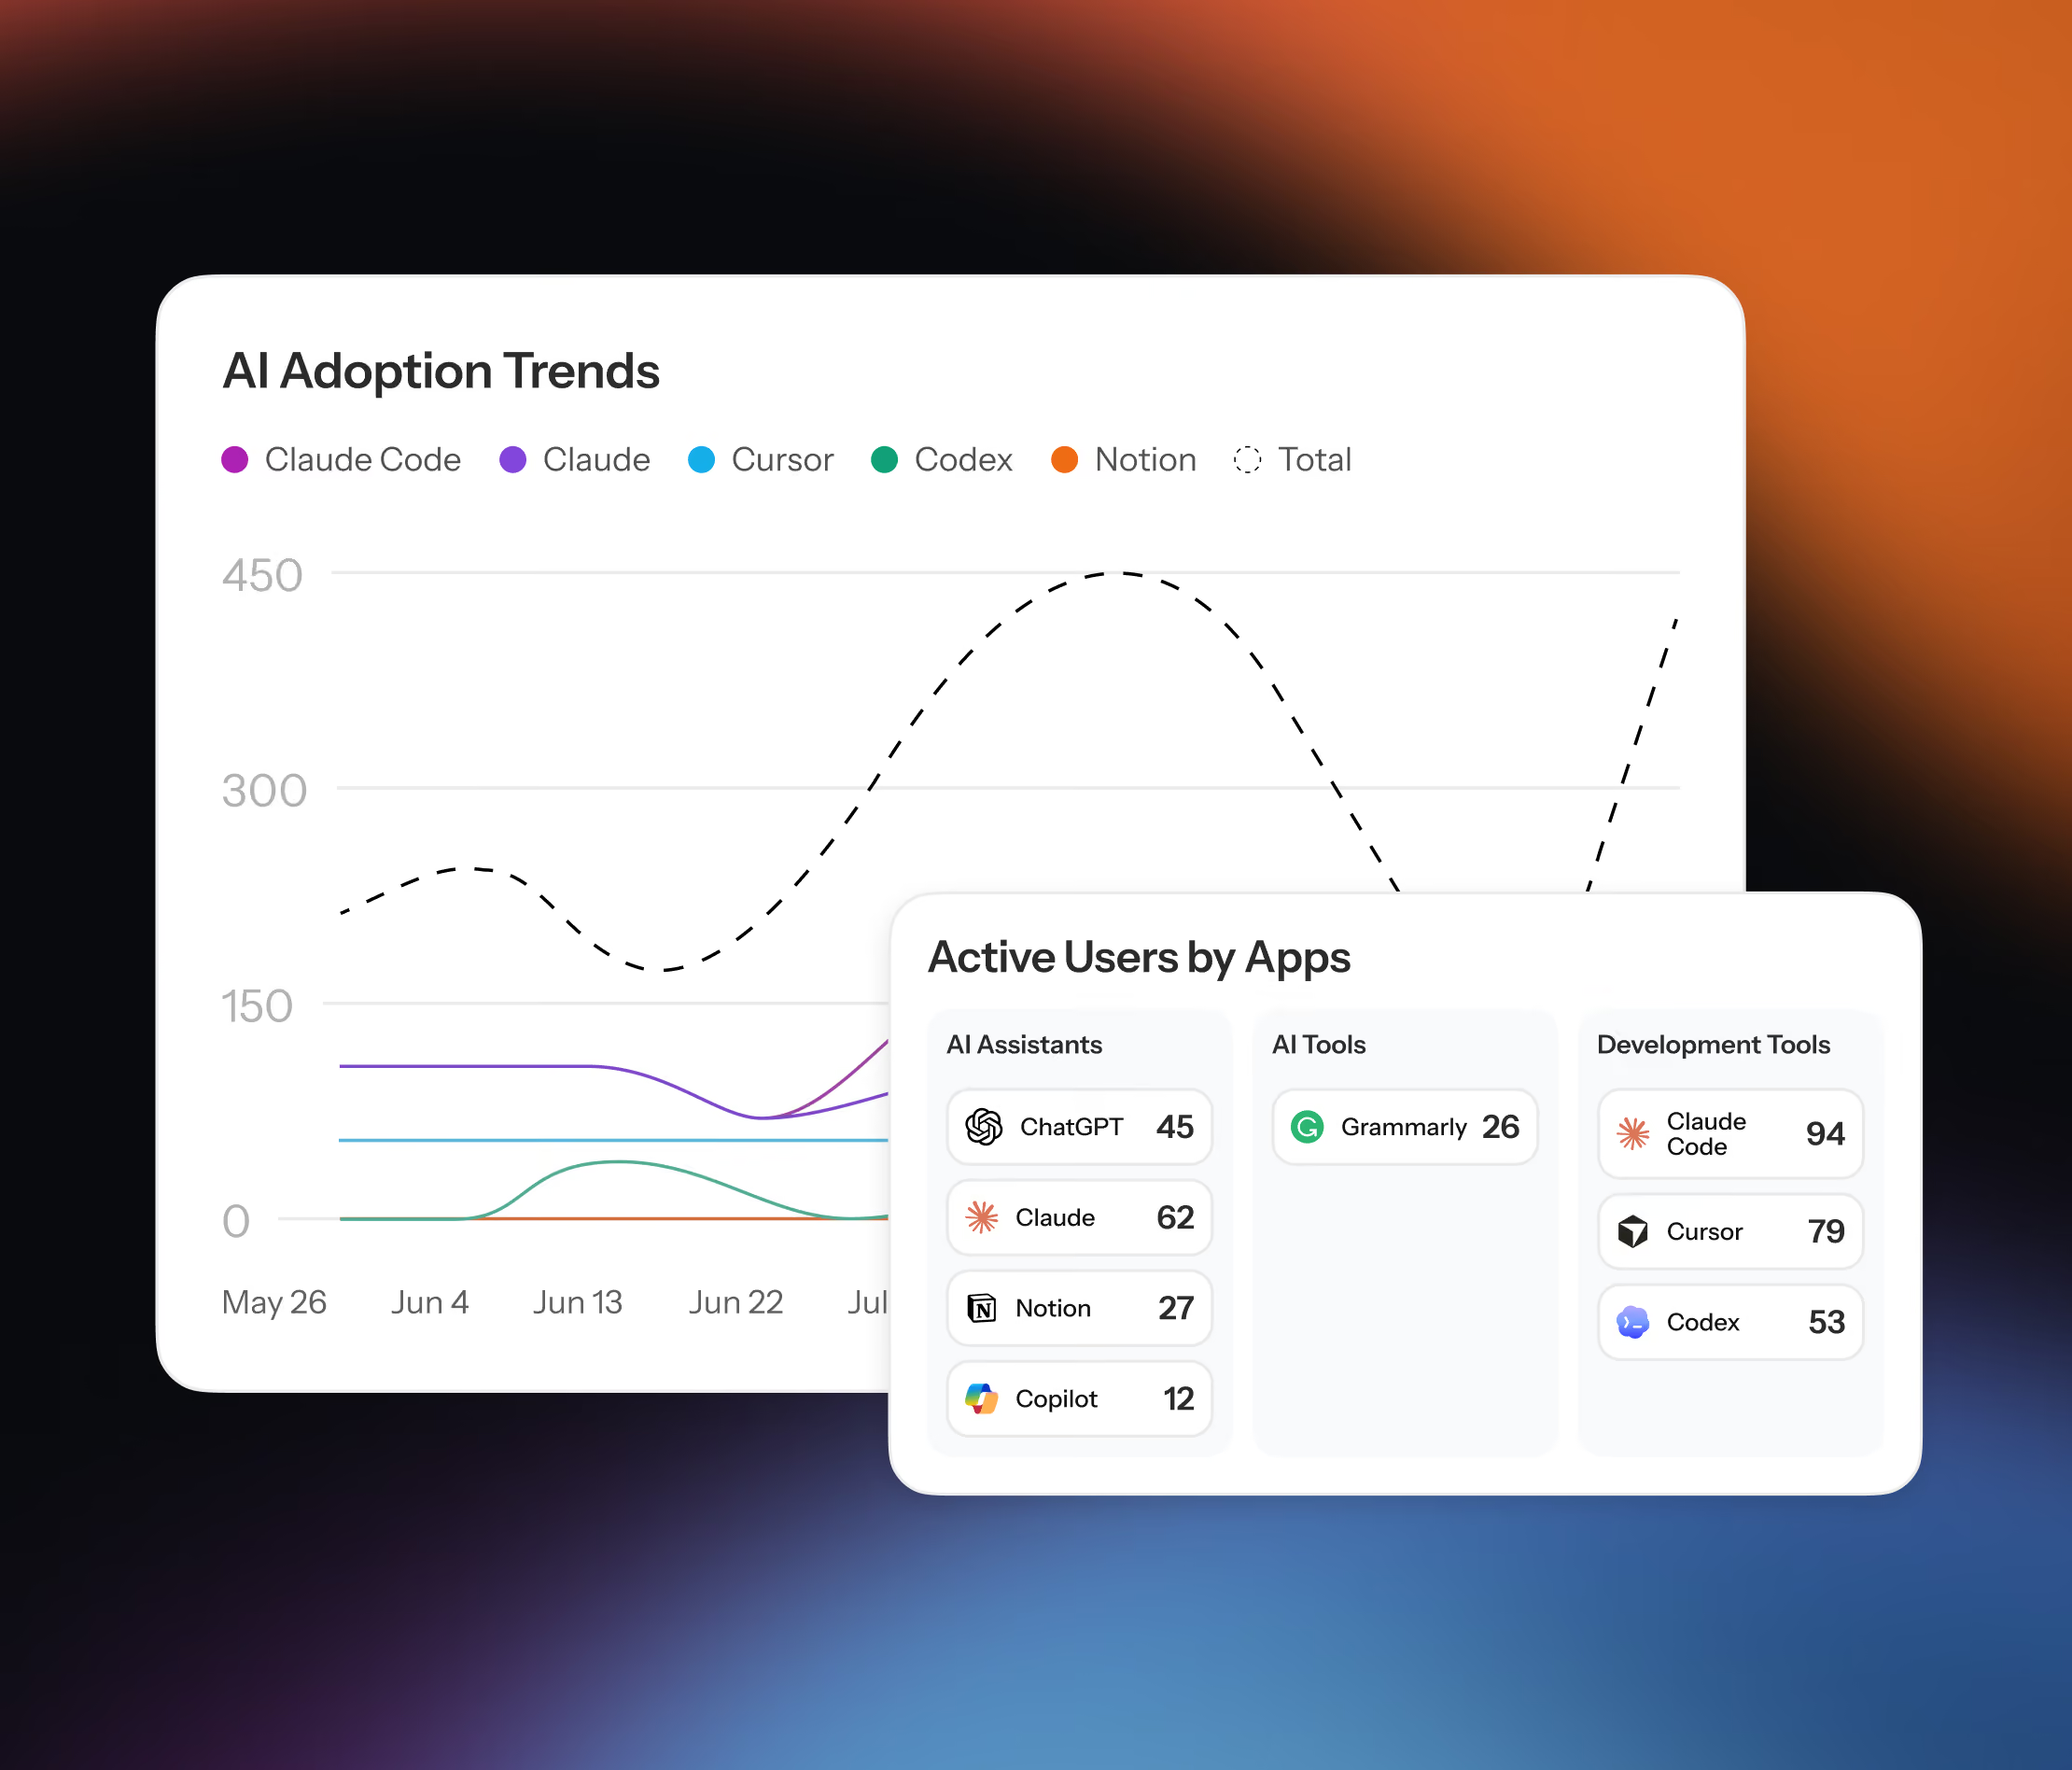
Employees adopt AI faster than any team can control, leading to shadow AI sprawl, non-compliant AI usage, and data exfiltration.

Unmanaged apps
Desktop AI tools encrypt their own traffic and bypass the proxy, leaving network and cloud tools with no view of them at all.
Ungoverned accounts
Approved AI tools are accessed through personal and guest identities that slip right past enterprise governance.
Uncontrolled data
Sensitive data gets pasted or uploaded into AI systems with no oversight of what's shared, where it goes, or how it can be used.
Unwatched MCPs
Internal and external MCP connections combine into data paths that no existing tool can see, let alone control.
The endpoint is where AI work is converging
Where a tool runs its AI decides whether it can govern AI in the moment or only report on it after.
Cloud & network tools
Sit off the device, so they never see desktop AI apps, local activity, or whether a human or an agent is acting.
Monitor-only governance
Detects and logs AI usage, but can't step in. By the time a policy violation surfaces, the data is already gone.
Runs the AI on the device, so it sees every interaction and acts on it. Bold coaches or blocks before data leaves, and keeps working offline.
A policy that can only watch is a record for the compliance file.
Only on-device AI can enforce it in the moment.
Only on-device AI can enforce it in the moment.
Three layers of AI control on the endpoint
Bold does it all: sees what's there, governs who can use it, and, most importantly, controls the data itself.
01
Complete AI Tool & Account Inventory
See the shadow AI, unmanaged accounts, and MCP connections your other tools can't, surfaced in one place.
AI applications (ChatGPT, Claude, Gemini, and others)
Desktop AI tools, including those with certificate pinning
MCPs, both managed and unmanaged
02
Identity & Usage Enforcement
Tie every AI interaction to a real user on an approved tool, even where encryption and certificate pinning leave other tools blind.
Approved AI tools only, no guest or anonymous sessions
Authentication with corporate-managed identities
No connections to personal or unmanaged MCPs
03
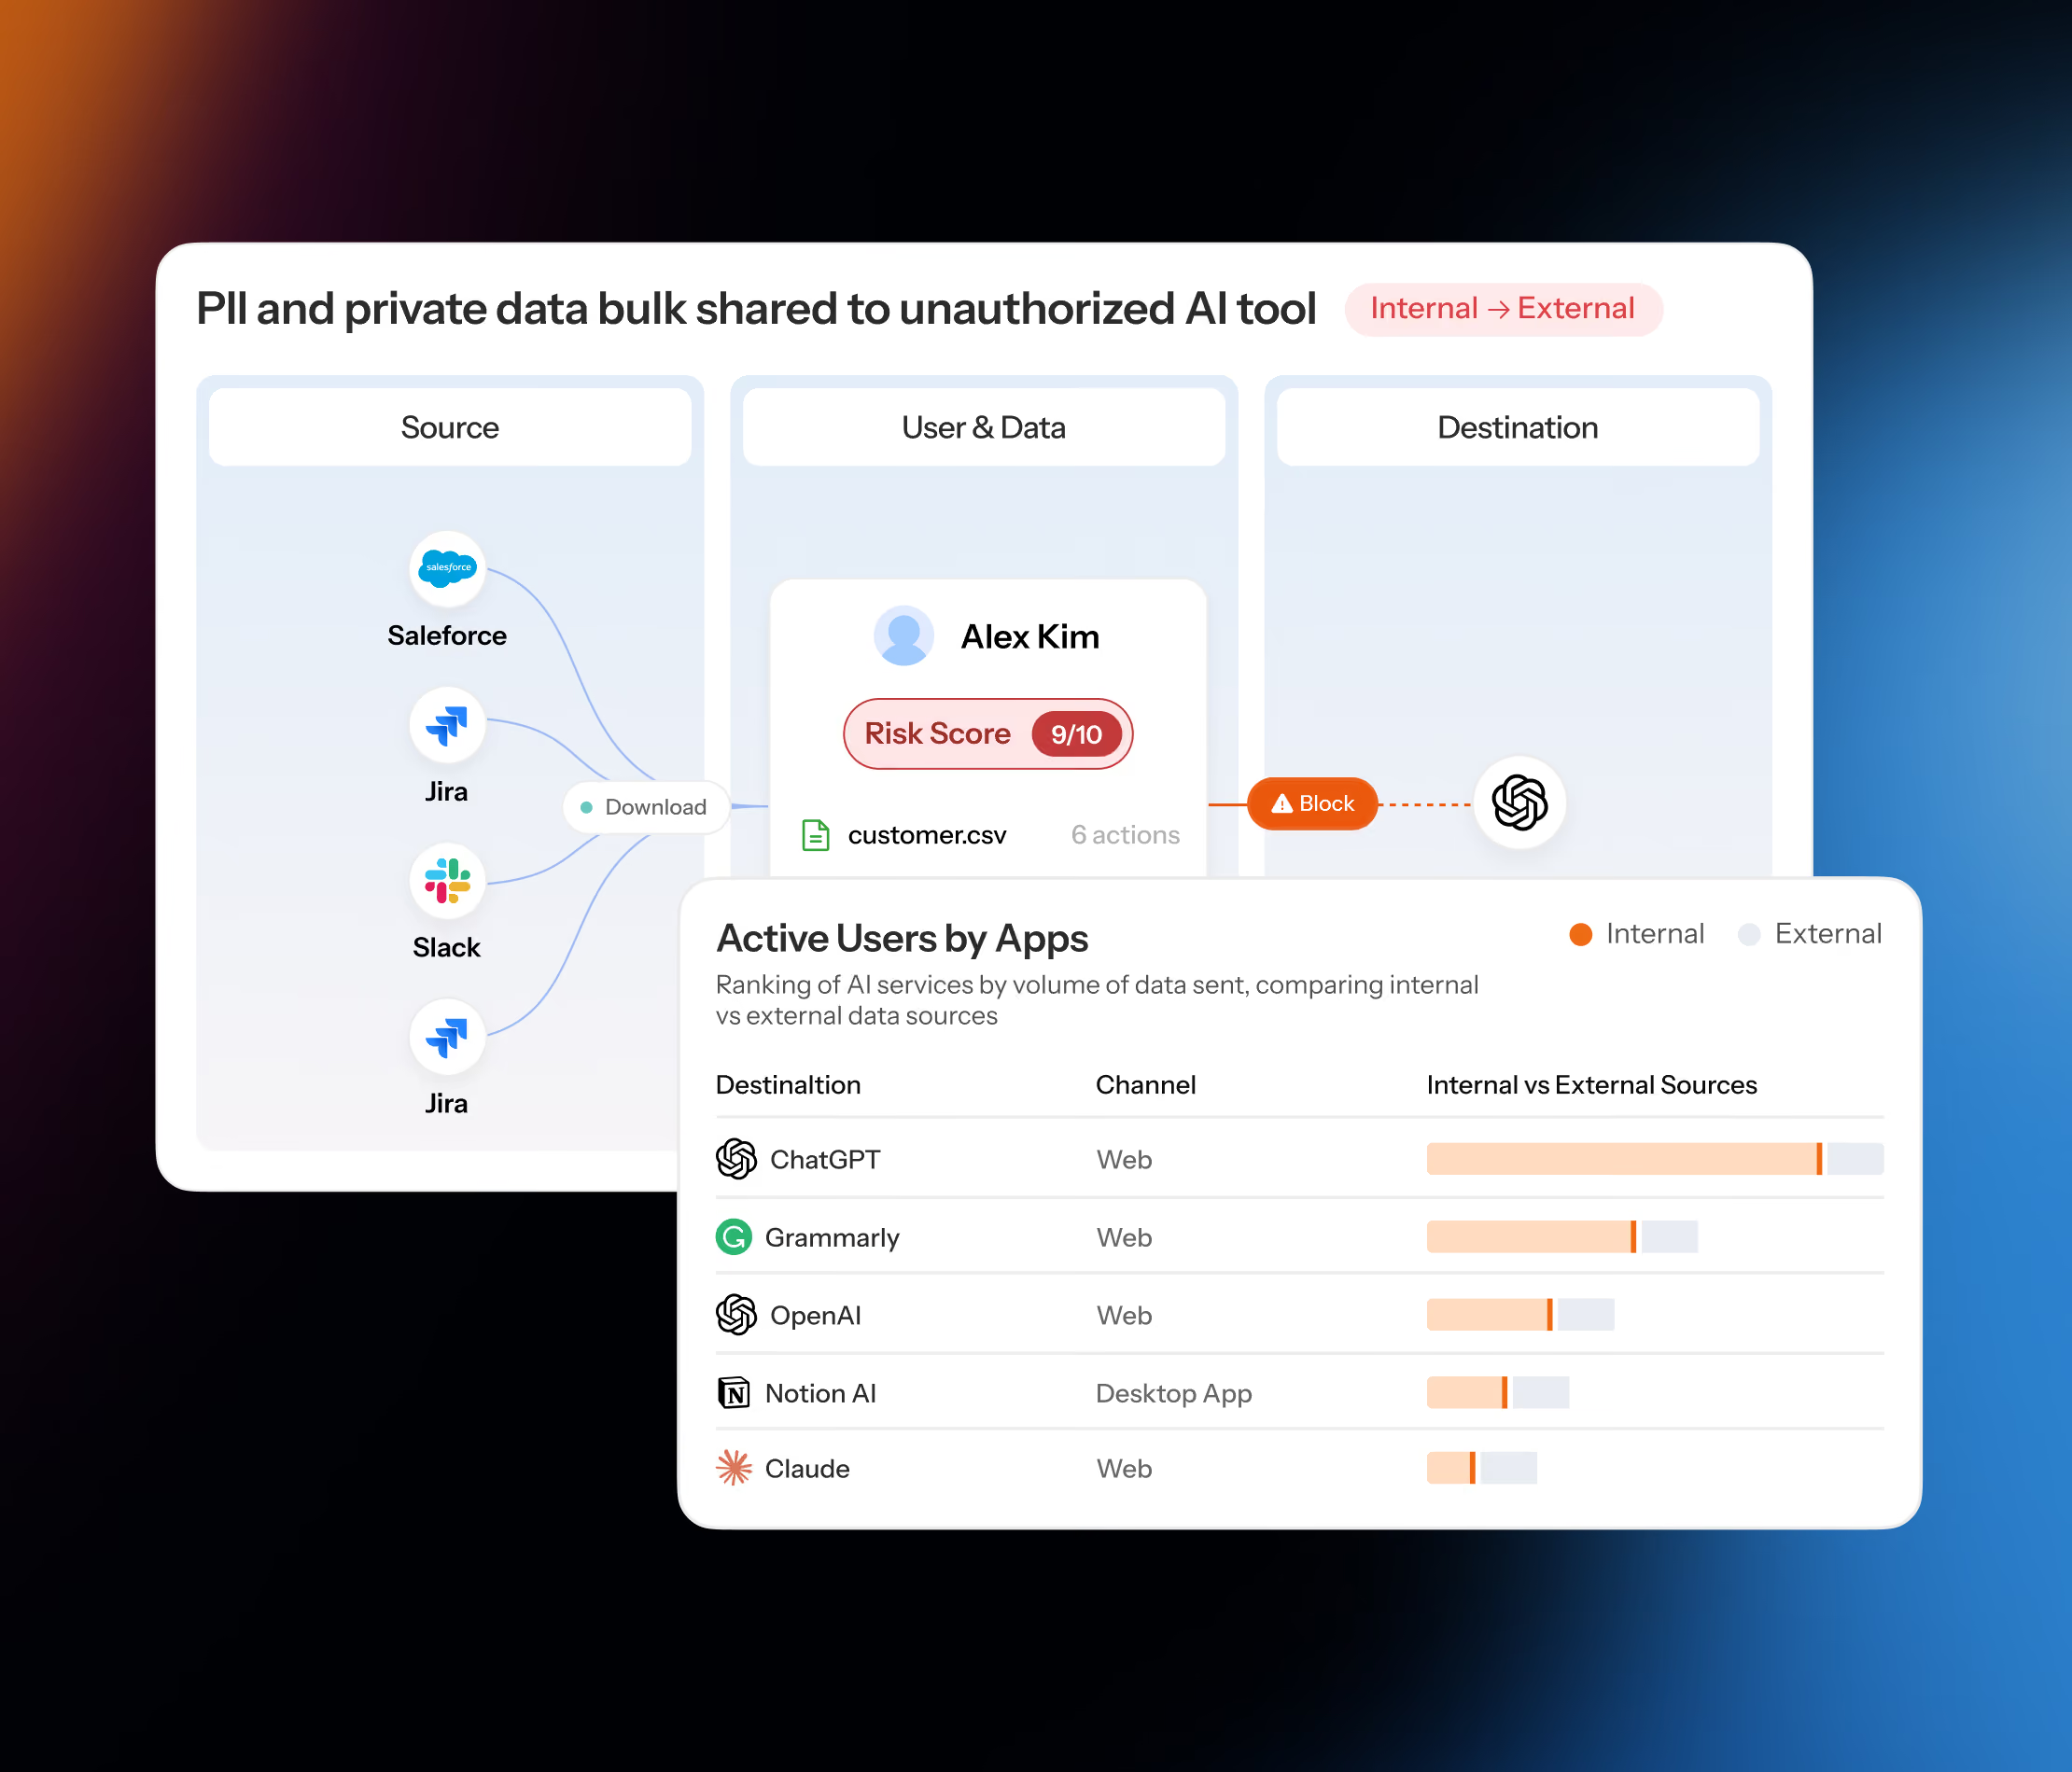
Data-Aware Session Control
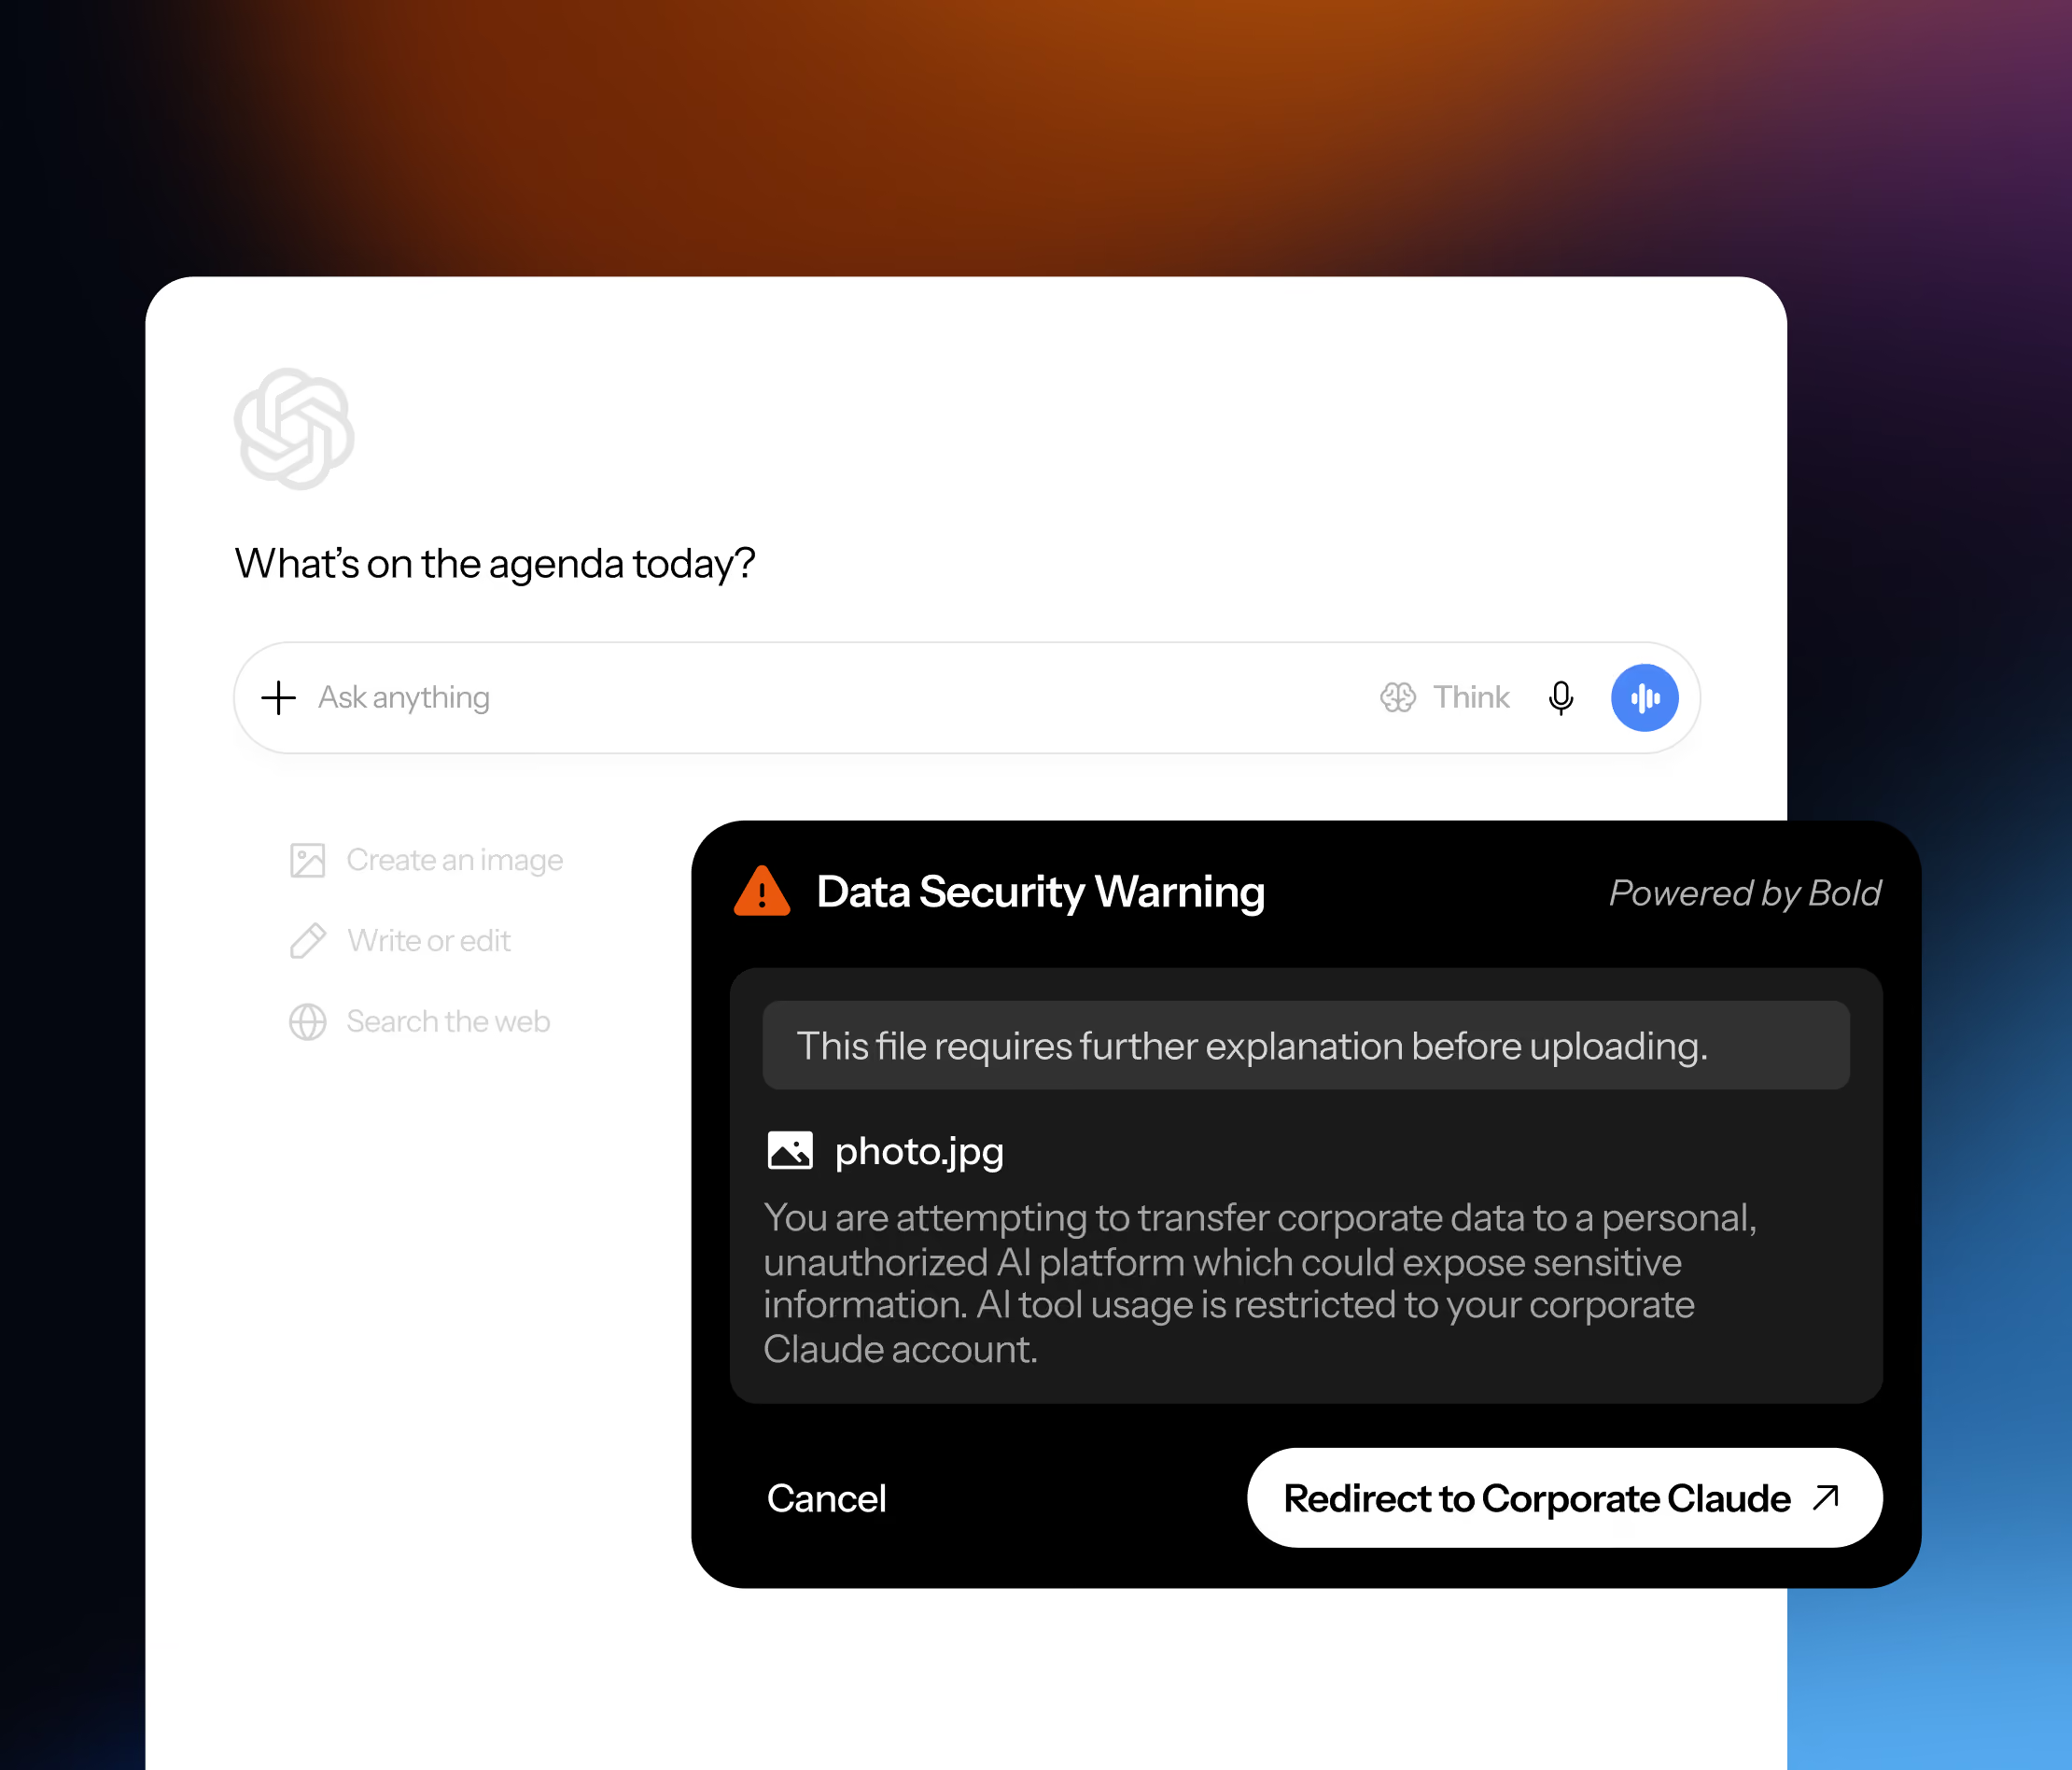
Coach, redirect, or block risky data at the moment of action, before it leaves the device, while legitimate work moves untouched.
Which data can be used with which AI tools
Sensitive data shared externally or with untrusted platforms
Data flow across internal and external AI systems
What changes when AI control runs on the device
Add the endpoint layer none of your network and cloud tools can see.
Unified AI visibility
Every tool, account, and MCP connection in one place, not stitched-together logs.
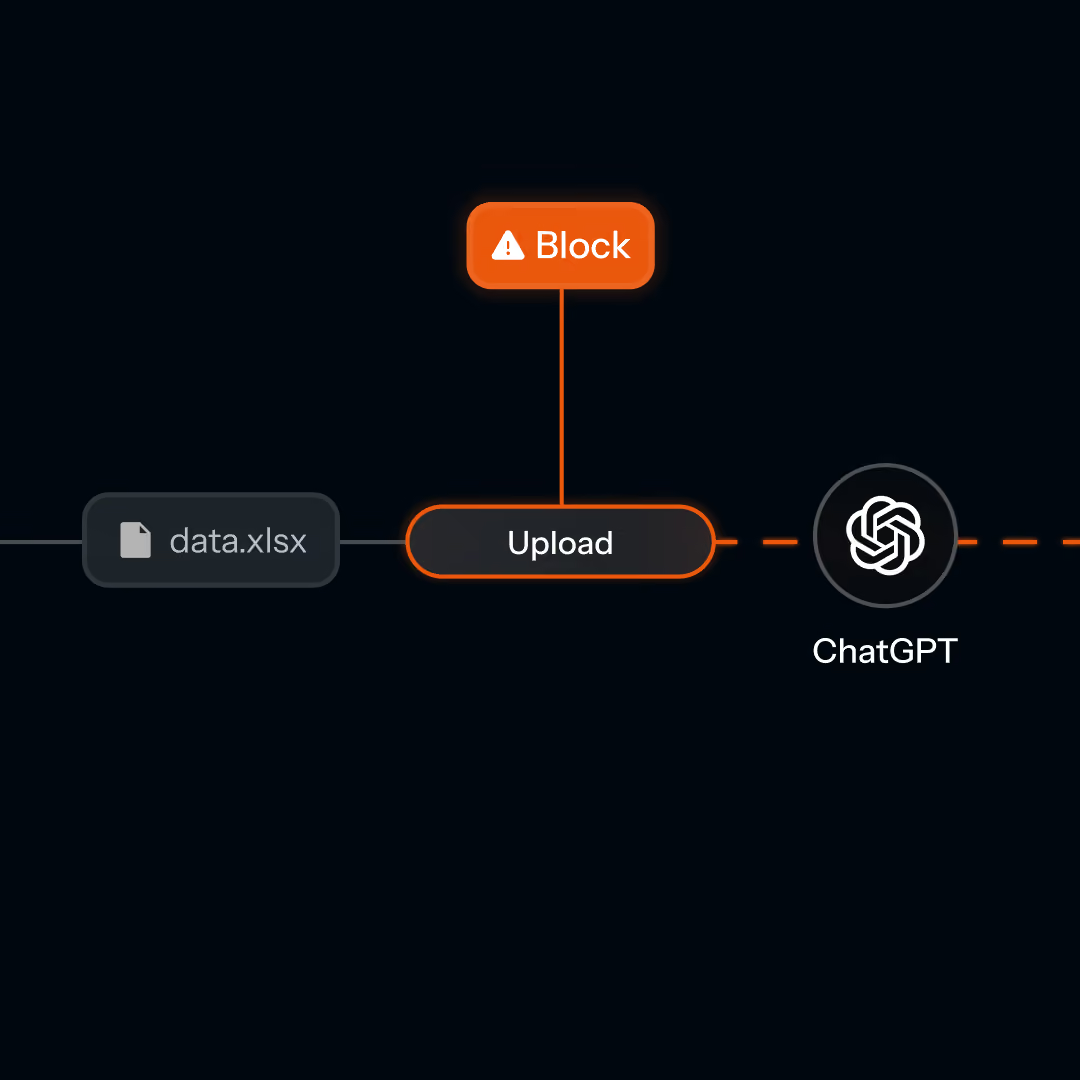
Real-time prevention
Risky data stopped before it leaves the device, not investigated after the fact.
Scalable protection
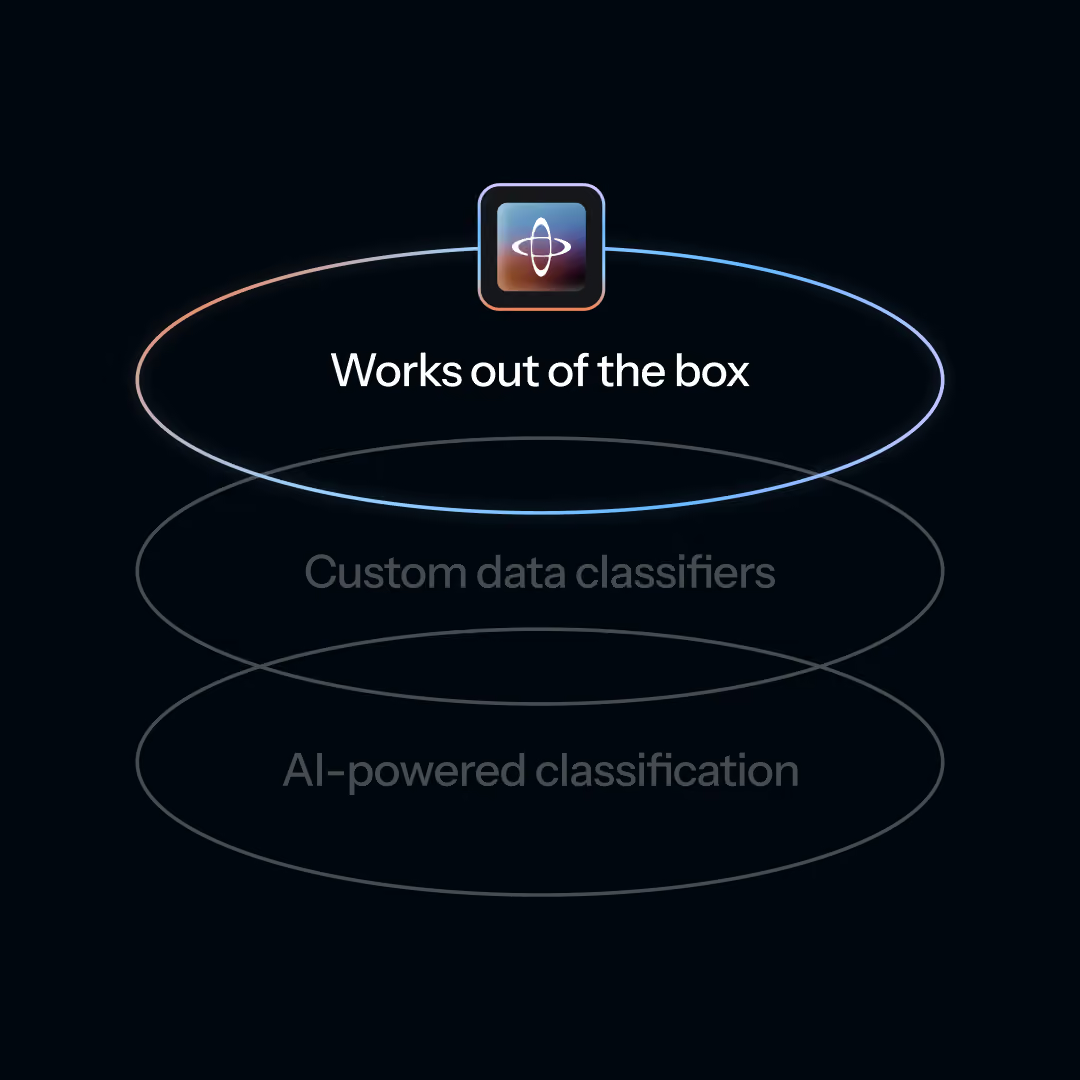
Classification and enforcement run automatically, so protection doesn't rely on team resources.
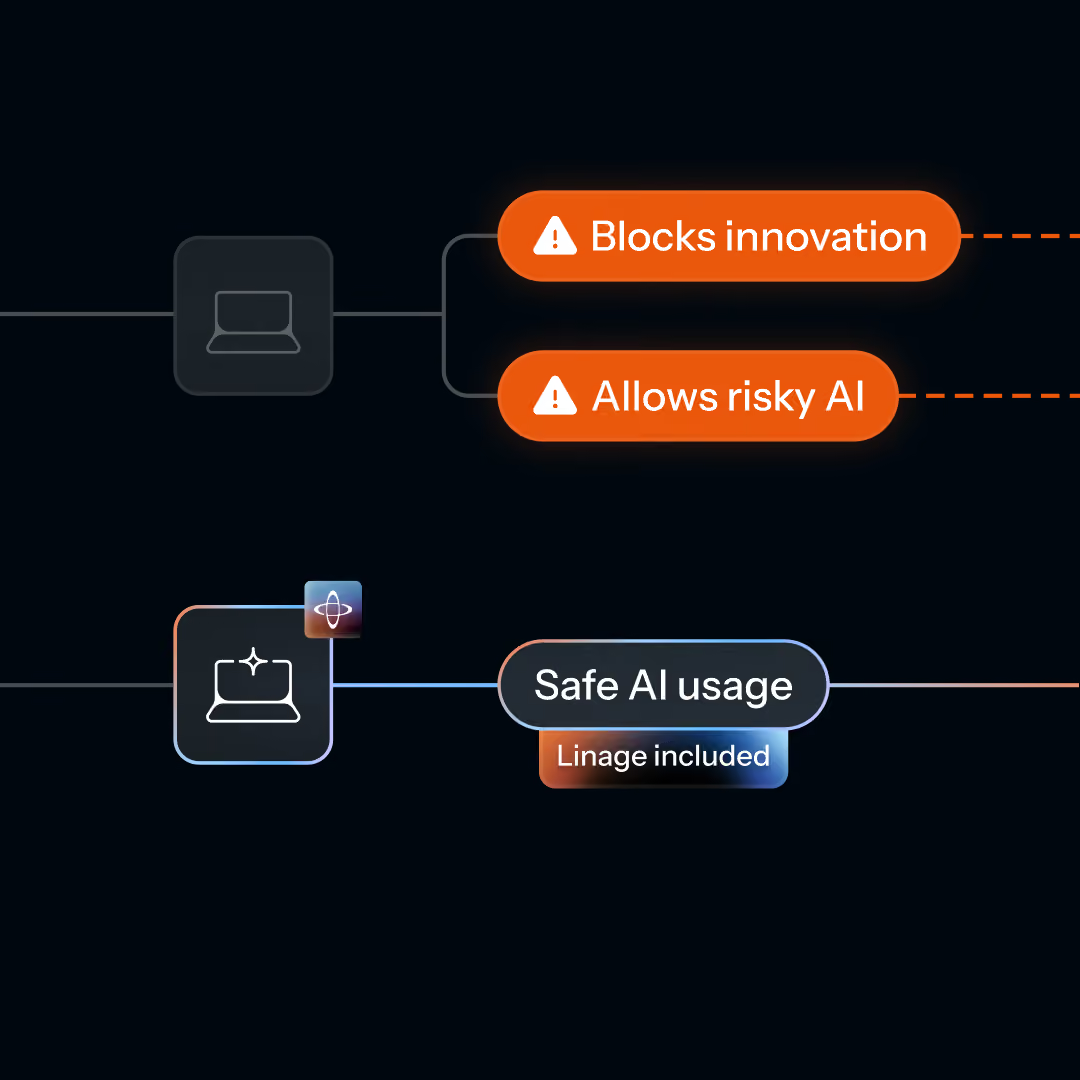
No AI tradeoffs
Real-time guardrails replace blanket bans, so the business moves fast without the risk.
One platform, three use cases
The same on-device classification that powers AI governance carries two more use cases from one deployment, drawing on one shared context.
Endpoint DLP
Semantic classification and real-time enforcement for sensitive data living and moving on the device.
AI Usage Control
See and govern every AI interaction on the device, including shadow AI and desktop apps cloud tools miss.
Endpoint Insider Risk
Behavioral intelligence plus data context, so every investigation carries the full picture from the start.