AI Security Meets Data Protection on the Endpoint
November 10 at 10AM PT | 1PM ET
Last year, AI security meant knowing which websites employees were visiting. Today, it means knowing and controlling what coding assistants and AI agents can read, write, and execute directly on a laptop, with local permissions and no proxy in the path. Latio’s 2026 AI Security Market Report puts it plainly: the first era of AI security was about controlling unapproved activity in the browser, and the second is about controlling it on endpoints.
That convergence is why DLP, insider risk, and AI governance now show up in the same report and in the same buying conversation. Three use cases, one layer, and a whole lot of vendors who sound very similar. If you’re confused, you’re not alone.
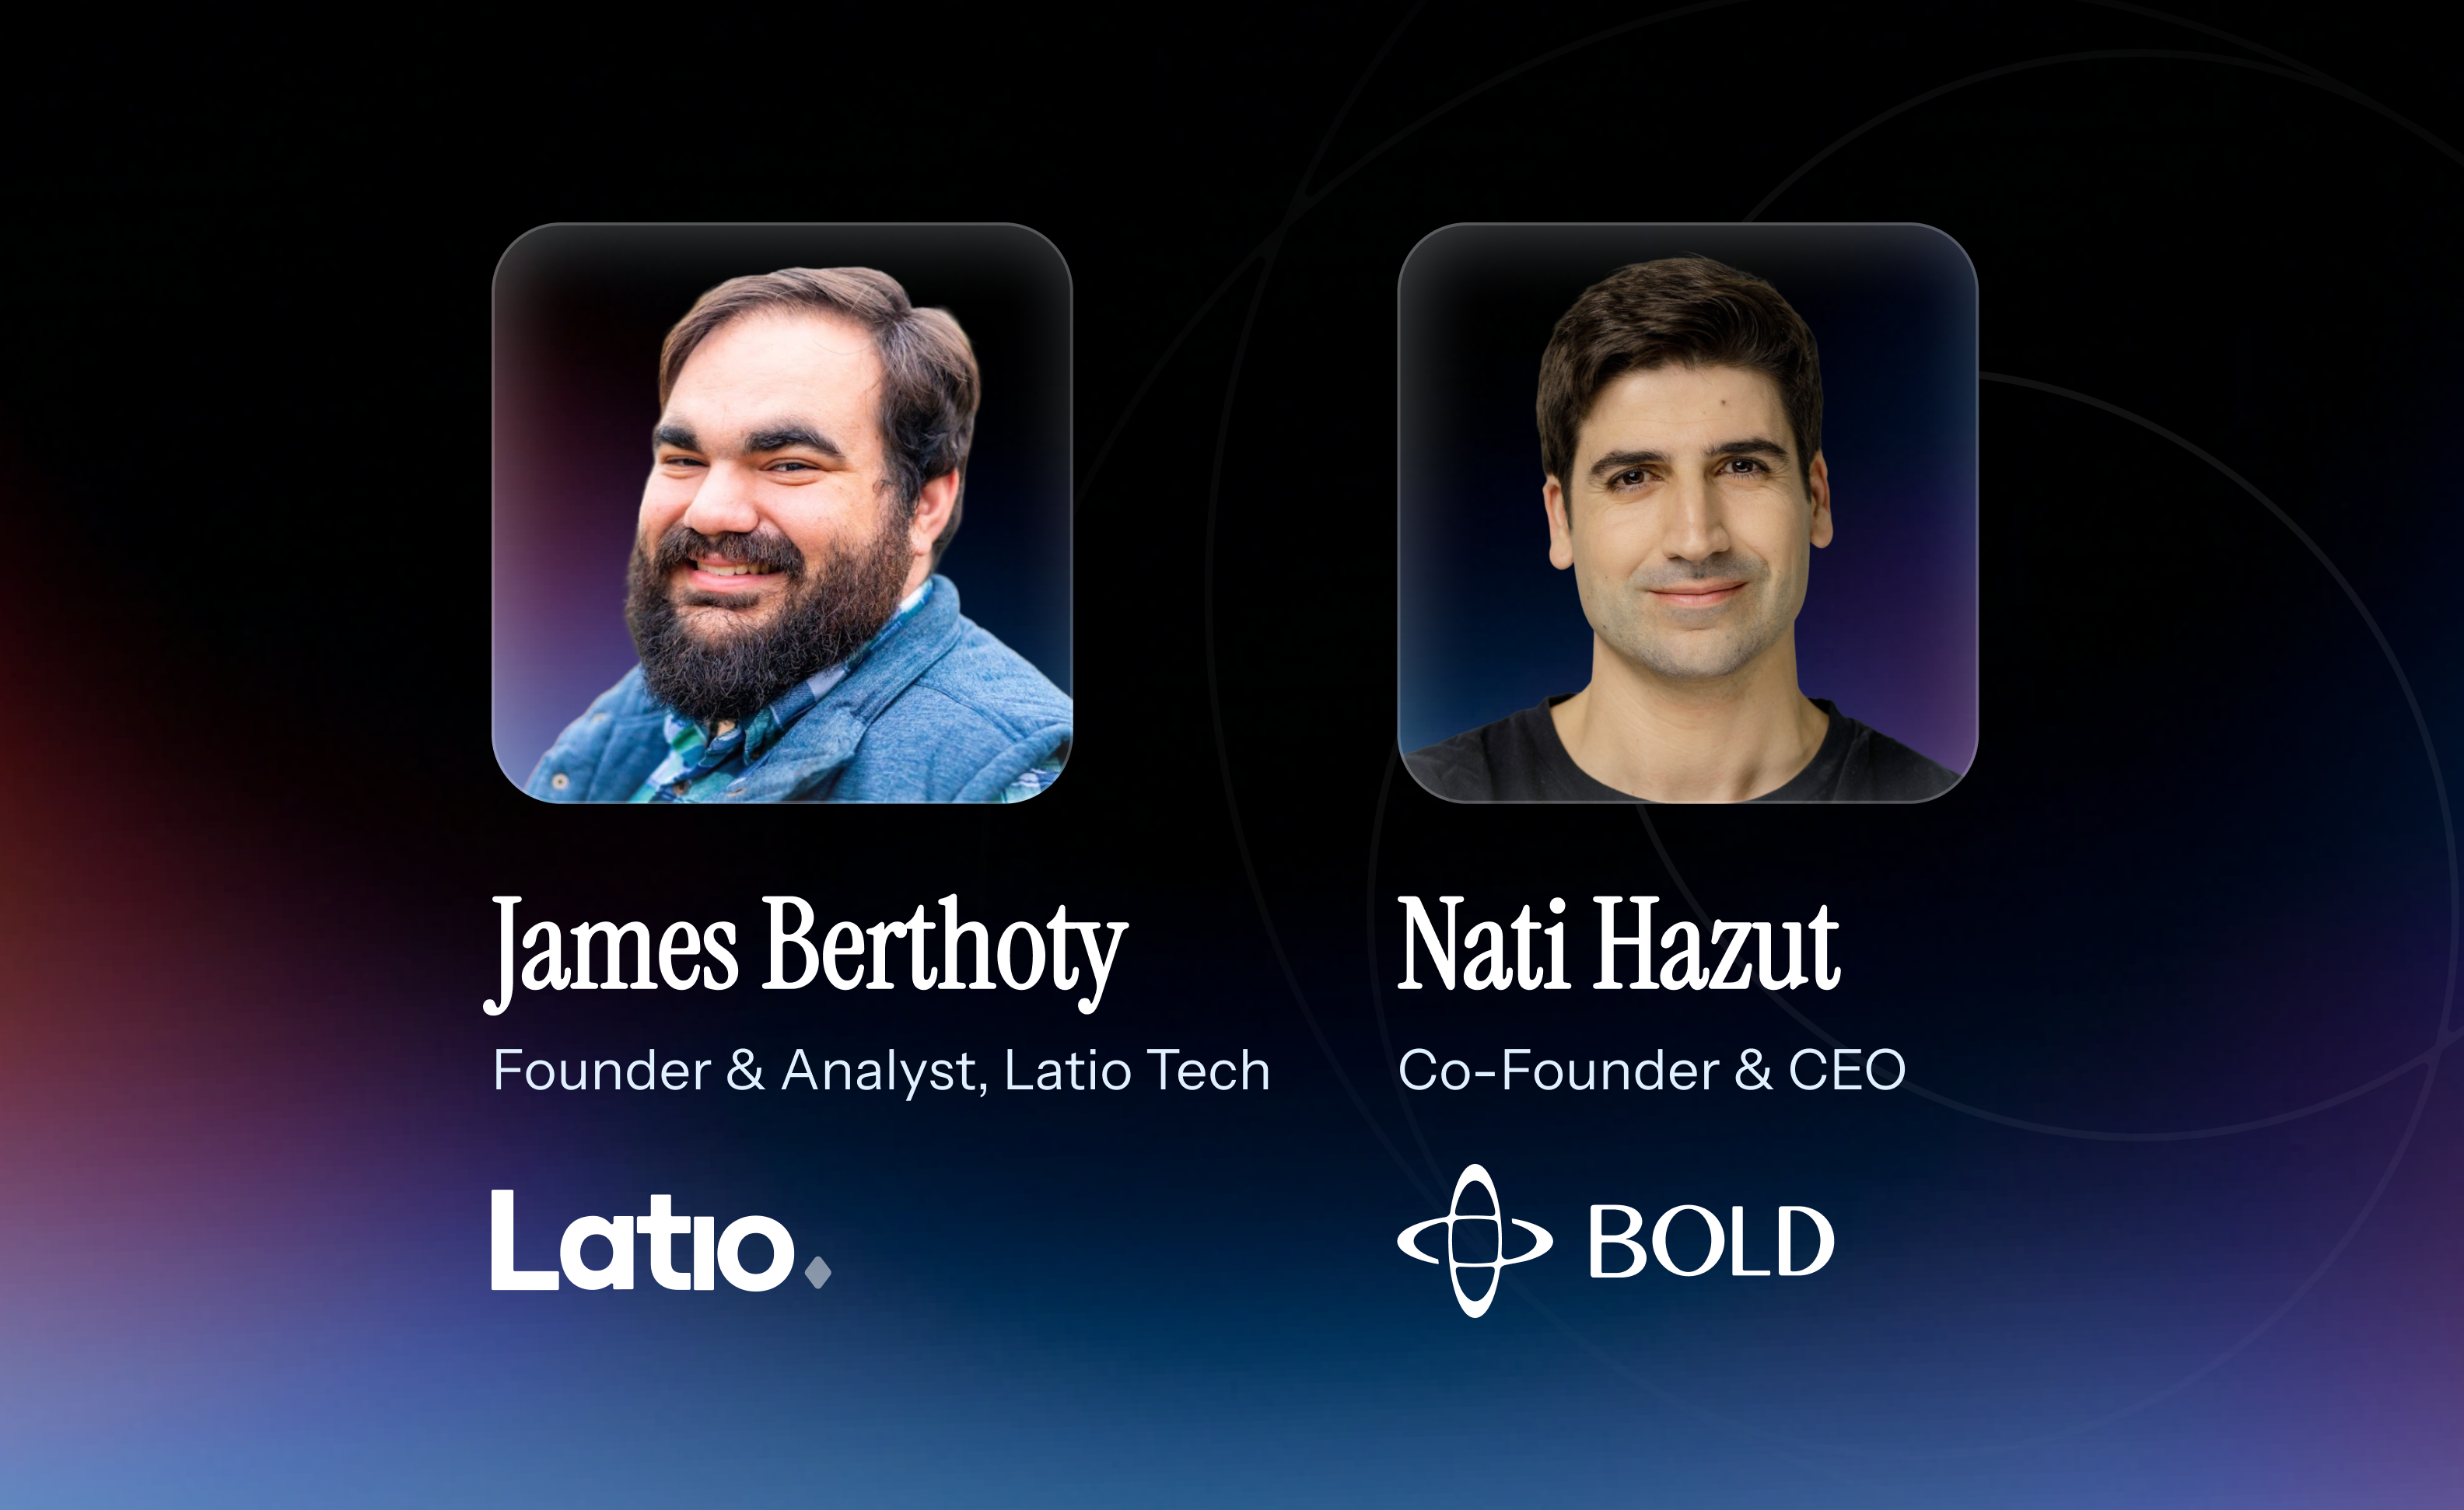
James Berthoty, founder of Latio and author of the report, joins Bold Co-Founder and CEO Nati Hazut to untangle it.
What will we cover?
- How the AI security market completely oreorganized around the endpoint in a single year
- Why DLP and insider risk resurfaced inside an AI security report, and what AI changed about both
- How to figure out which problem you have (AI, data, or endpoint) and evaluate vendors to meet your goals
Who should join?
- Security leaders rolling out AI without visibility into how it's being used on employee devices
- Data protection and DLP owners whose tools were built for a different set of channels
- Insider risk teams watching AI change how data moves
- Anyone evaluating vendors in this space and trying to tell the categories apart